IP Tunnel Explained: How Tunneling Works
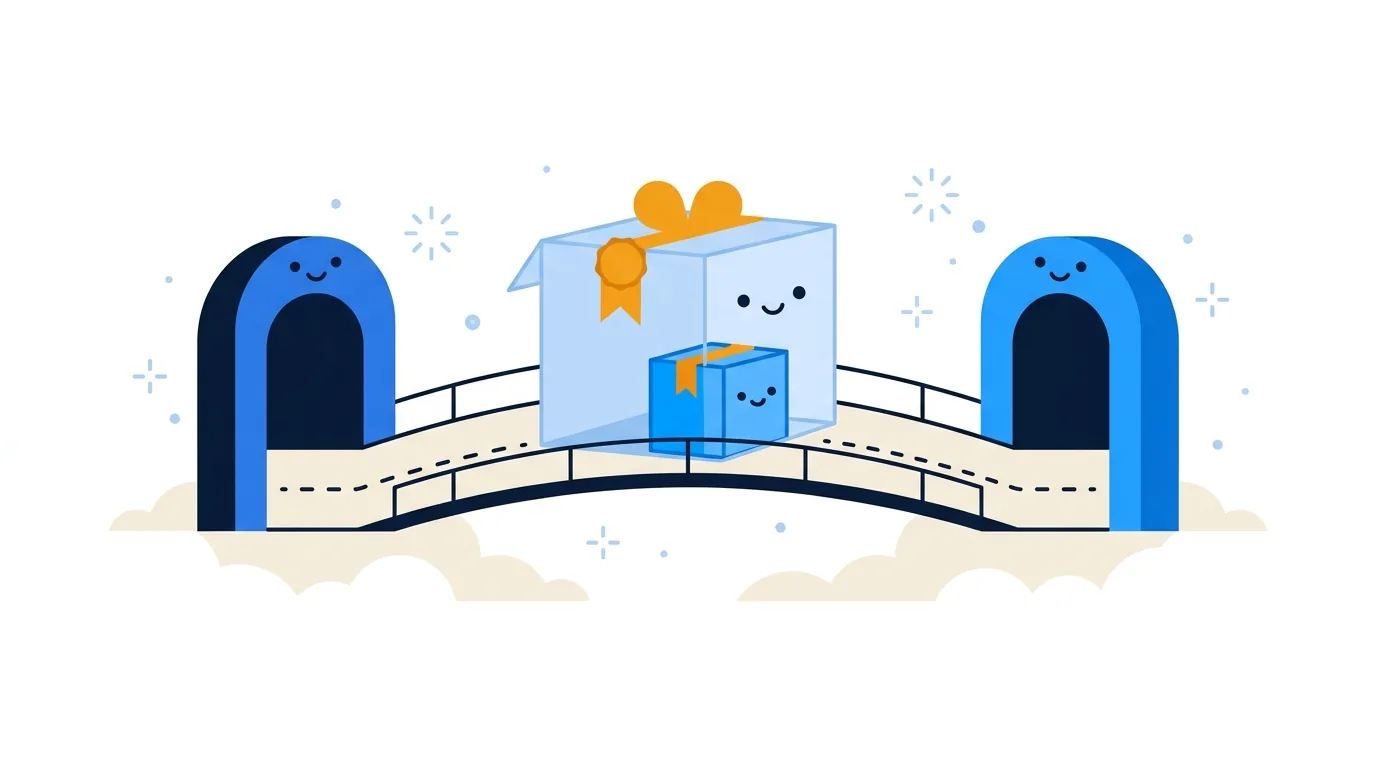
An IP tunnel carries packets from one endpoint to another by wrapping each original packet inside a new packet that can cross an intermediate network. It can connect private networks or carry IPv6 across IPv4, but the wrapping alone does not encrypt anything. So ask two questions: what protocol wraps the traffic, and what protects it?
A site-to-site tunnel may join two offices while your ordinary web traffic still leaves through your ISP. A full-tunnel VPN usually sends that traffic to a VPN gateway first. Loqmi’s IP check shows which public exit address a website sees.
What an IP tunnel does
Think of a packet as a labeled parcel. Its inner IP header names the original sender and final destination. A tunnel endpoint puts it inside an outer packet addressed to the far endpoint. Transit routers forward using that outer header. The other endpoint removes it and routes the original packet onward.
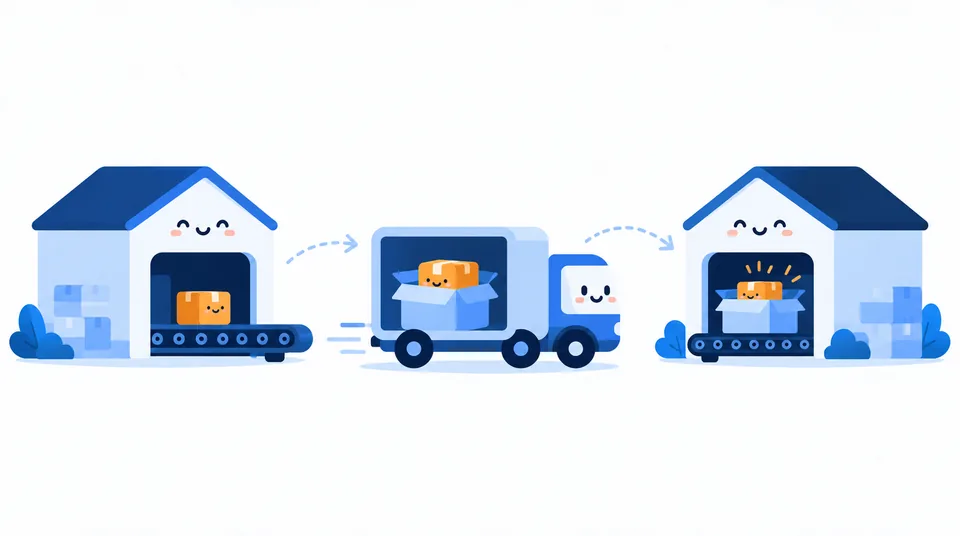
For example, a laptop at office A can send from private address 10.20.0.25 to an office B server at 10.40.0.8. The first router wraps the packet in one addressed to B’s public gateway. That gateway unwraps it and forwards the inner packet. These example private addresses are from the ranges reserved by RFC 1918.
This process is encapsulation: one packet inside another. Both endpoints need matching tunnel settings and routes. The tunnel is a virtual link that runs over existing networks (the ocean already has plenty of cables).
Why networks use tunnels
Tunnels connect networks without a direct route and can carry IPv6 across an IPv4-only segment. The IETF describes tunneling as one transition option alongside dual stack and translation in RFC 7059.
Endpoints need reachable outer addresses and routes. NAT (Network Address Translation) rewrites address information at a router, so its firewall must allow the tunnel protocol. DHCP (Dynamic Host Configuration Protocol) can assign changing addresses, and a tunnel set up for an old endpoint address may stop working. Your ISP (internet service provider) carries outer packets but does not automatically secure them.
Regional Internet Registries (RIRs) hand out public address blocks, while private addresses can be reused on separate networks. Two offices using overlapping private ranges may need routing changes or translation. See public vs. private IP addresses.
Common IP tunnel protocols
“Tunnel” names a method, not a protocol (yes, the word is doing a lot of work). The protocol decides what can be carried and whether it adds security.
| Protocol or setup | What it is useful for | Security note |
|---|---|---|
| IP-in-IP | Simple IP packet inside another IP packet; useful for straightforward routing or IPv4/IPv6 transitions. | Encapsulation only. It does not encrypt the inner packet. RFC 2003 defines IPv4-in-IPv4. |
| GRE | Generic Routing Encapsulation can carry different network-layer protocols and is often used between routers. | GRE does not provide encryption by itself. Its base format is specified in RFC 2784. |
| IPsec tunnel mode | Protects traffic between hosts or network gateways, commonly for VPN connections. | Provides security services when configured with suitable authentication and encryption; it is more than packet wrapping. See RFC 4301. |
| GRE protected by IPsec | Useful where GRE carries traffic or routing information and IPsec protects it across an untrusted network. | Two jobs are being done: GRE carries; IPsec protects. Both ends must agree on both layers. |
A VPN is not another word for tunnel. It creates a private network over shared infrastructure, often using a tunnel plus security controls. An unencrypted GRE tunnel is not private in the confidentiality sense. The tunnel is the envelope and encryption is the lock.
Choose the right approach
Pick the option that fits the job. Actual support varies by router, firewall, and operating system.
| Your goal | Reasonable starting point | Check before deployment |
|---|---|---|
| Carry IPv6 through an IPv4-only link | A configured IPv6-over-IPv4 tunnel, GRE, or a supported tunnel service. | Endpoint reachability, provider support, and whether the path allows the required IP protocol. |
| Connect two IP subnets with minimal features | IP-in-IP where both endpoints support it. | Whether you need multicast, non-IP payloads, or security; basic IP-in-IP supplies none of those extras. |
| Carry routing protocols or varied payloads | GRE, often paired with IPsec on an untrusted path. | Firewall handling, routing loops, MTU, and IPsec configuration. |
| Protect remote access or site-to-site traffic | A properly configured IPsec VPN or another VPN with authenticated encryption. | Which traffic uses the tunnel, where it exits, and how credentials and keys are managed. |
Check whether native IPv6, dual stack, or ordinary routing solves the problem with fewer moving parts. Each extra layer adds configuration to explain during an outage (never a popular time for archaeology).
What tunneling does not guarantee
A tunnel does not automatically encrypt traffic or hide the outer endpoint. A transit provider can generally see outer addresses and traffic timing. Without encryption, anyone inspecting the path may also see the encapsulated content. IPsec can encrypt the inner packet, but the outer delivery details remain.
Not every tunnel changes your public IP. A full-tunnel VPN may send web traffic through its gateway; split tunneling sends only selected traffic there. A router-to-router tunnel may carry office traffic while web browsing still exits through your ISP. See how to check whether a VPN is working.
IP-based location is an estimate, not GPS. Address allocation and ISP routing affect databases, so a city can be wrong. A remote tunnel endpoint changes the estimate only for traffic routed through it. See why an IP location can be wrong.
Spot common tunnel problems
If a tunnel is up but applications misbehave, check routes and packet size. Encapsulation uses part of the path’s maximum transmission unit (MTU), the largest packet a link can carry without fragmentation. Cisco documents a GRE-over-IPv4 case that adds 24 bytes. On a 1,500-byte path, 1,476 bytes remain for the inner packet. That is one example, not a universal GRE overhead, because options and outer IPv6 change the total.
| Symptom | Possible cause | Useful check |
|---|---|---|
| Tunnel interface is up, but remote subnet is unreachable | Missing route, wrong inner subnet, or a firewall rule blocking inner traffic. | Check the route table and test the tunnel endpoint separately from the destination host. |
| Small requests work; large transfers stall | MTU or path MTU discovery problem after headers are added. | Compare packet size with the tunnel MTU; review ICMP “fragmentation needed” or Packet Too Big handling. |
| Tunnel never establishes across a home router | NAT or firewall may not pass the tunnel protocol, or the endpoint address changed. | Check router support, firewall logs, and the configured outer addresses. NAT traversal support is protocol-dependent. |
| Websites still show the ISP address | Only selected routes use the tunnel, or it connects networks without changing internet egress. | Check routing policy and compare the public address before and after with Loqmi’s IP checker. |
Note your address on Loqmi with the tunnel off, connect it, then refresh. A changed address means the browser used another public exit. An unchanged address does not prove failure if the tunnel carries only private traffic. Test reachability with an allowed host inside the remote subnet too.
Quick diagnosis: Separate the question “is the tunnel endpoint reachable?” from “is this destination routed through it?” and “is the traffic encrypted?” Those are three different checks, even when a dashboard puts them next to one green light.
Key takeaways
- An IP tunnel wraps a packet in another packet so it can cross a network that cannot route the original directly.
- IP-in-IP and GRE provide encapsulation; neither encrypts traffic on its own.
- IPsec can add authentication and encryption, but the exact security depends on configuration.
- Check routes, endpoint reachability, NAT/firewall handling, and MTU separately when troubleshooting.
- Use a public-IP check to see the browser’s exit address. It does not prove that every tunnel route works.
Frequently asked questions
Is an IP tunnel the same as a VPN?
No. A tunnel is a way to carry packets between endpoints, while a VPN is a private network built over another network and usually includes authentication and encryption. Some tunnels, such as basic GRE or IP-in-IP, do not encrypt traffic by themselves. Check the protocol and its security settings rather than relying on the word tunnel.
Can an IP tunnel work through NAT?
Sometimes. NAT changes address information, but support depends on the tunnel protocol and the router or firewall. Protocols without TCP or UDP ports, such as plain GRE or IPv6-in-IPv4, may need explicit firewall or NAT support. IPsec can use NAT traversal, but both endpoints must be configured for it.
Why does a tunnel lower my internet speed?
Encapsulation adds headers, leaving less room for application data in each packet. Encryption may also use device or gateway processing, and a longer route to the tunnel endpoint can add delay. A mismatch between tunnel MTU and the path MTU can cause fragmentation or dropped packets, so compare speed and packet behavior with the tunnel on and off.
Does an IP tunnel hide my location?
Not automatically. A site sees the public address used by the connection that reaches it. With a full-tunnel VPN, that is often the VPN gateway address; with a site-to-site or split tunnel, ordinary web traffic may still leave through your ISP. IP-based location is approximate and does not identify a precise street address.
Sources
- RFC 7059: A Comparison of IPv6-over-IPv4 Tunnel Mechanisms
- RFC 2784: Generic Routing Encapsulation (GRE)
- RFC 2003: IP Encapsulation within IP
- RFC 4301: Security Architecture for the Internet Protocol
- RFC 1918: Address Allocation for Private Internets
- Cisco: Resolve IPv4 Fragmentation, MTU, MSS, and PMTUD Issues with GRE and IPsec
- Red Hat Enterprise Linux: Configuring IP tunnels
Related articles
Ghost IP Address: What It Means and How to Check
Ghost IP is informal networking shorthand, not one defined address type. Learn the three common meanings and how to check which one you are seeing.
Validate IP Address: IPv4 and IPv6 Rules
Check IPv4 and IPv6 syntax, understand common validation errors, and separate a well-formed address from one that is public or reachable.
Private Network: Addresses, Access, and Safety
Understand private networks, private IP ranges, and how your devices reach the internet. Includes a quick public-IP and CGNAT check.