CIDR notation IP address: ranges and subnets
CIDR notation writes an IP address followed by a slash and a prefix length, such as 192.168.1.77/26. The prefix tells you how many leading bits identify the network. The remaining bits pick the addresses inside it. Read it correctly and you can find the whole range, the network boundary, and (for ordinary IPv4 subnets) the usable host addresses.
CIDR notation IP address: what the slash means
CIDR means Classless Inter-Domain Routing. It replaced the old habit of guessing network size from address “classes” with an explicit prefix length. In IPv4, the address has 32 bits (which sounded roomy at the time). /24 means the first 24 bits are the network prefix, and the remaining 8 bits vary within the block. The same slash notation works for IPv6, whose addresses have 128 bits. RFC 4632 defines IPv4 prefix notation and its role in routing.
The prefix counts bits, not dots or octets. A /24 lines up neatly with three IPv4 octets, but /26 cuts through the last octet. A bigger prefix number means a smaller block, which is the opposite of what most people expect from a bigger number. More bits are fixed for the network, so fewer are left for devices. Old class labels still come up in conversation, but modern networks use the explicit prefix.
For a familiar example, 192.168.1.0/24 has mask 255.255.255.0 and covers 192.168.1.0 through 192.168.1.255. That is 256 total addresses. In a normal IPv4 subnet, the first address names the network and the last is the broadcast address. That leaves 254 hosts you can assign.
How to read an IP range from CIDR
Subtract the prefix from the address width to get the host-bit count, then raise two to that power to get the block size. For IPv4, a /26 leaves 32 − 26 = 6 host bits, so the block contains 2⁶ = 64 addresses. A /24 leaves 8 bits and contains 256. That formula gives total addresses, not automatically the number you can assign to devices.
When the prefix ends inside an octet, the mask shows the boundary. A /26 mask is 255.255.255.192. The final mask octet is 192, so the blocks advance by 256 − 192 = 64: .0, .64, .128, and .192. Think of each block as a row of numbered seats. The prefix tells you where one row ends, even if the address you were handed sits in the middle.
| IPv4 prefix | Subnet mask | Total addresses | Usable hosts in a typical subnet |
|---|---|---|---|
/24 | 255.255.255.0 | 256 | 254 |
/25 | 255.255.255.128 | 128 | 126 |
/26 | 255.255.255.192 | 64 | 62 |
/27 | 255.255.255.224 | 32 | 30 |
/30 | 255.255.255.252 | 4 | 2 |
The “usable” column assumes a conventional IPv4 subnet with separate network and broadcast addresses. Point-to-point links are a special case, covered below.
A worked CIDR range example
Suppose a device is configured as 192.168.1.77/26. This is an IP address in CIDR notation, but it is not the network address, because its host portion is nonzero. The /26 blocks in the last octet span 0 to 63, 64 to 127, 128 to 191, and 192 to 255. Since 77 falls in 64 to 127, the network is 192.168.1.64/26 and the full CIDR notation range is 192.168.1.64–192.168.1.127.
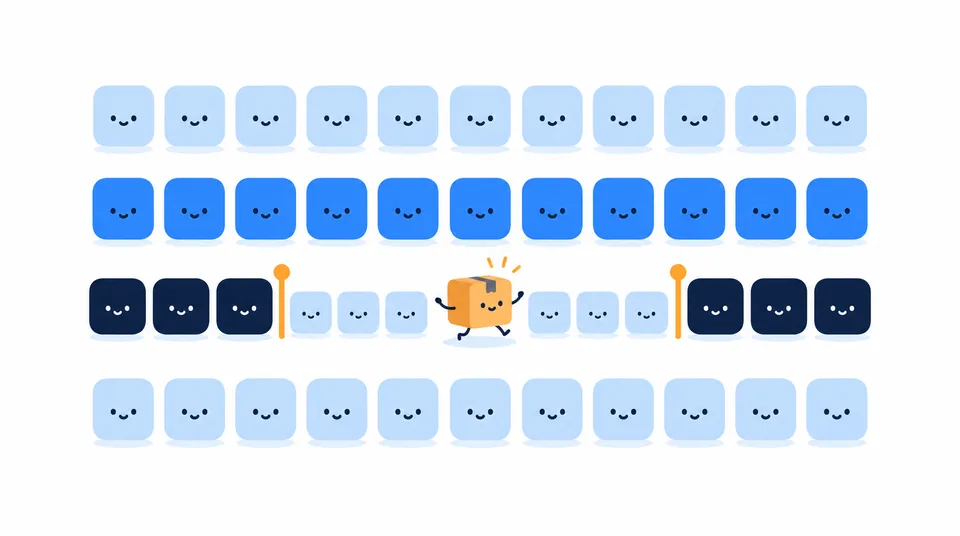
- Network address:
192.168.1.64, with host bits set to zero. - Broadcast address:
192.168.1.127, with host bits set to one. - Typical usable host range:
192.168.1.65–192.168.1.126, or 62 addresses.
This normalization step is the one people skip most often. If you see 192.168.1.77/26 in a device setting, do not report .77 as the start of the subnet. For another example, the IPv4 address guide explains the four-octet structure. The Loqmi homepage shows the public IP your browser uses on the internet, and that address is separate from your router’s local subnet.
CIDR and subnet planning
Subnetting means dividing one address block into smaller blocks. Each time you add one to the prefix, you borrow one host bit. The block size halves, and the number of equal subnets doubles. Split 192.168.1.0/24 into /26 blocks and you get four ranges, each with 64 total IPv4 addresses and typically 62 host addresses. This helps when you want office computers, guest Wi-Fi, and printers on separate networks (your printer will not miss the guest Wi-Fi chatter).
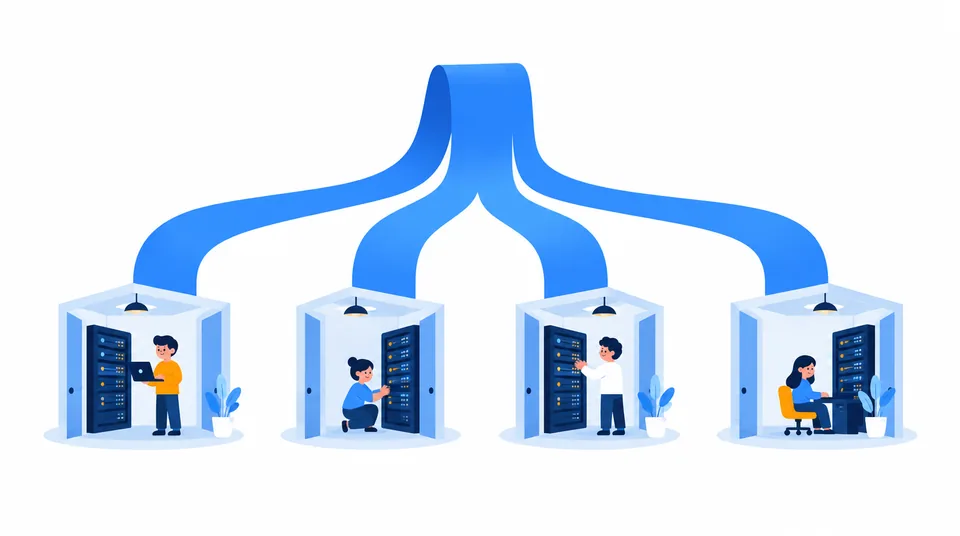
When choosing a size, count addresses your design actually needs, including gateways and infrastructure, then leave sensible room for growth. CIDR is also used to combine adjacent routes into a shorter advertisement, called route aggregation. Routers generally choose the most specific matching route when routes overlap, which is why a /26 can take precedence over a broader /24; “most specific” means the longer prefix, not the more important network. RFC 4632 describes longest-match forwarding.
Private IPv4 space is also written in CIDR. RFC 1918 reserves 10.0.0.0/8, 172.16.0.0/12, and 192.168.0.0/16 for private internets. Your home router commonly uses one of these ranges on the LAN side and uses NAT (Network Address Translation) to share a public address. If you want to distinguish the router’s local address from the public one, see public vs. private IP addresses.
CIDR prefixes in IPv6
IPv6 uses the same prefix idea with 128 address bits. In 2001:db8:1234::/48, the first 48 bits identify the prefix, and every address under it shares those leading bits. RFC 4291 defines IPv6 addressing. IPv6 has no broadcast addresses, because multicast handles group communication instead. So the IPv4 rule “subtract two” does not apply to IPv6 host counts.
You will often see a /64 used for an IPv6 subnet on a link. A prefix length marks a boundary, though. It does not promise how many devices your ISP or network will provide. An ISP may delegate a larger block, such as a /56, so a home network can number multiple /64 links. Actual allocation depends on the network provider and configuration. The address space is huge, so the hard part is usually documenting it clearly rather than rationing each address.
Exceptions and common CIDR mistakes
Do not treat “network address plus broadcast address are unavailable” as a law for every IPv4 prefix. On a point-to-point link, /31 can use both addresses as endpoints; RFC 3021 specifies this exception. A /32 identifies one IPv4 address, often as a host route, rather than a normal range of hosts.
| What you see | What it means | Useful check |
|---|---|---|
| Address does not end at a neat .0 | It may be a host address inside a subnet | Calculate the network boundary from the prefix |
| More digits after the slash | Smaller block, fewer host bits | Use 2^(address bits − prefix) for total size |
| Host count seems two too low | You may be counting a normal IPv4 subnet | Check whether it is a /31 point-to-point link or a /32 route |
| IPv6 host count uses “minus two” | That IPv4 shortcut does not apply | IPv6 has no broadcast address |
A prefix alone also does not tell you whether an address is public, private, or assigned to your device. It describes a range. DHCP (Dynamic Host Configuration Protocol) can assign a local address and prefix to a device, while your ISP routes or delegates public address space; those are related jobs, and the slash reveals neither one. CIDR is a map scale, not a location tracker.
Quick self-check: compare the public address shown on Loqmi with the local address shown in your device’s network settings. They may differ because your router performs NAT. A speed test at Loqmi’s speed test measures connection performance; it does not determine your subnet prefix.
Key takeaways
- The slash number is the count of leading network bits; it is explicit in both IPv4 and IPv6.
- For IPv4, total addresses equal
2^(32 − prefix); ordinary host counts usually exclude network and broadcast addresses. - Find the block containing the given address before naming its network or usable range.
- IPv6 has no broadcast address, and IPv4 /31 point-to-point links are an exception to the usual subtract-two shortcut.
Frequently asked questions
Can a CIDR prefix be written without an IP address?
Yes. A prefix such as /24 can describe a block size or a route filter when the network itself is understood from context. For an actual subnet or route, write both the network address and prefix, such as 192.0.2.0/24, so the block is unambiguous.
Does a larger CIDR number mean a larger IP range?
No. A larger prefix number fixes more bits as the network portion and leaves fewer bits for addresses inside the block. For example, /26 is smaller than /24: it contains 64 IPv4 addresses, while /24 contains 256. The slash number is a bit count, so it works without class-based address assumptions.
Can CIDR tell me whether an IP address is public?
CIDR tells you the boundaries of a block, not its public or private status by itself. Some prefixes are reserved for private or other special purposes, while many others are globally routable. Check the address against an authoritative registry or use a trusted lookup; an address alone does not reveal a precise home address.
What does 0.0.0.0/0 mean?
In IPv4 routing, 0.0.0.0/0 is the default route: its zero-bit prefix matches any IPv4 destination that has no more specific route. It is a routing instruction, not a claim that every address belongs to one local network. IPv6 has the analogous default prefix ::/0.
Sources
Related articles
Ghost IP Address: What It Means and How to Check
Ghost IP is informal networking shorthand, not one defined address type. Learn the three common meanings and how to check which one you are seeing.
Validate IP Address: IPv4 and IPv6 Rules
Check IPv4 and IPv6 syntax, understand common validation errors, and separate a well-formed address from one that is public or reachable.
Private Network: Addresses, Access, and Safety
Understand private networks, private IP ranges, and how your devices reach the internet. Includes a quick public-IP and CGNAT check.